Every vulnerability class gets its own expert agent.

Canima deploys vulnerability-specific AI agents deep into your apps: SPAs, REST APIs, GraphQL and WebSockets, every parameter and every authentication flow. Full OWASP Top 10 coverage and beyond, with proof-of-concept evidence for every confirmed finding.

webapp · app.example.com
$ canima agent deploy --scope webapp
[*] Target: https://app.example.com
[*] Spider: 847 endpoints mapped
[+] SQLi (blind time-based): /api/users?id=1
Payload: 1' AND SLEEP(5)-- -
Response: 5.02s delay confirmed
[+] XSS (stored): /comments POST body
Context: HTML attribute injection
[+] IDOR: /api/orders/{id} → user B data
[!] 14 confirmed vulnerabilities found
340+
Specialized agents
OWASP Top 10
And beyond
100%
Findings with PoC
Every role
Authenticated testing
01 / Coverage

Full application coverage, beyond DAST.

A generic scanner runs the same checks against every parameter. Canima assigns a dedicated AI agent to each vulnerability class, an agent that thinks only about SQL injection, or only about XSS, or only about SSRF, eliminating context rot and catching what scanners miss.

Injection Attacks

Dedicated agents for SQL injection (6 techniques: error-based, UNION, blind boolean, blind time-based, stacked queries, out-of-band), OS command injection, NoSQL injection (MongoDB operators, JavaScript injection), and server-side template injection across Jinja2, Twig, Freemarker, and more. Each technique gets its own payload generation and detection logic.

SQLi (6 techniques)OS Command InjectionNoSQL InjectionSSTI
Cross-Site Scripting (XSS)

Specialized XSS agents test reflected, stored, and DOM-based vectors with context-aware payload generation. The agent understands HTML context (attribute, tag, JavaScript block, URL) and crafts payloads that match the injection point. Advanced fuzzing with encoding bypass, WAF evasion, and mutation-based payload generation for edge cases that template scanners miss.

Reflected XSSStored XSSDOM-based XSSWAF Bypass

Authentication & Authorization

JWT vulnerability testing covers algorithm confusion (none, HS256/RS256 swap), claim tampering, weak signing keys, and token expiration bypass. IDOR testing across all identified object references with automated privilege escalation checks. Session management analysis includes fixation, prediction, and improper invalidation. Mass assignment and hidden parameter discovery via parameter fuzzing.

JWT AttacksIDORPrivilege EscalationSession Flaws

SSRF & Server-Side Attacks

SSRF agents test for internal service access, cloud metadata endpoint exposure (AWS IMDSv1/v2, GCP, Azure), protocol smuggling (gopher, file, dict), and DNS rebinding. XXE injection testing across XML parsers with out-of-band data exfiltration. Insecure deserialization detection for Java (ObjectInputStream), Python (pickle), YAML, and JSON formats.

SSRFCloud MetadataXXEDeserialization

API & Modern Architecture Testing

GraphQL testing covers introspection abuse, query complexity attacks (depth/breadth), batching attacks, and authorization bypass on nested resolvers. REST API testing includes method tampering, content-type confusion, and rate limiting bypass. WebSocket security testing for injection via message frames and cross-site WebSocket hijacking. HTTP request smuggling across CL.TE, TE.CL, and TE.TE desynchronization variants.

GraphQLREST APIsWebSocketsRequest Smuggling

Configuration & Infrastructure

Security header analysis validates CSP directives, HSTS preload status, X-Frame-Options, Referrer-Policy, and Permissions-Policy. CORS misconfiguration detection with origin reflection and null origin testing. Host header injection and cache poisoning assessment. Open redirect detection with chaining analysis, finding where a redirect can be leveraged as a stepping stone for phishing or token theft.

Security HeadersCORSCache PoisoningOpen Redirects
In the portal

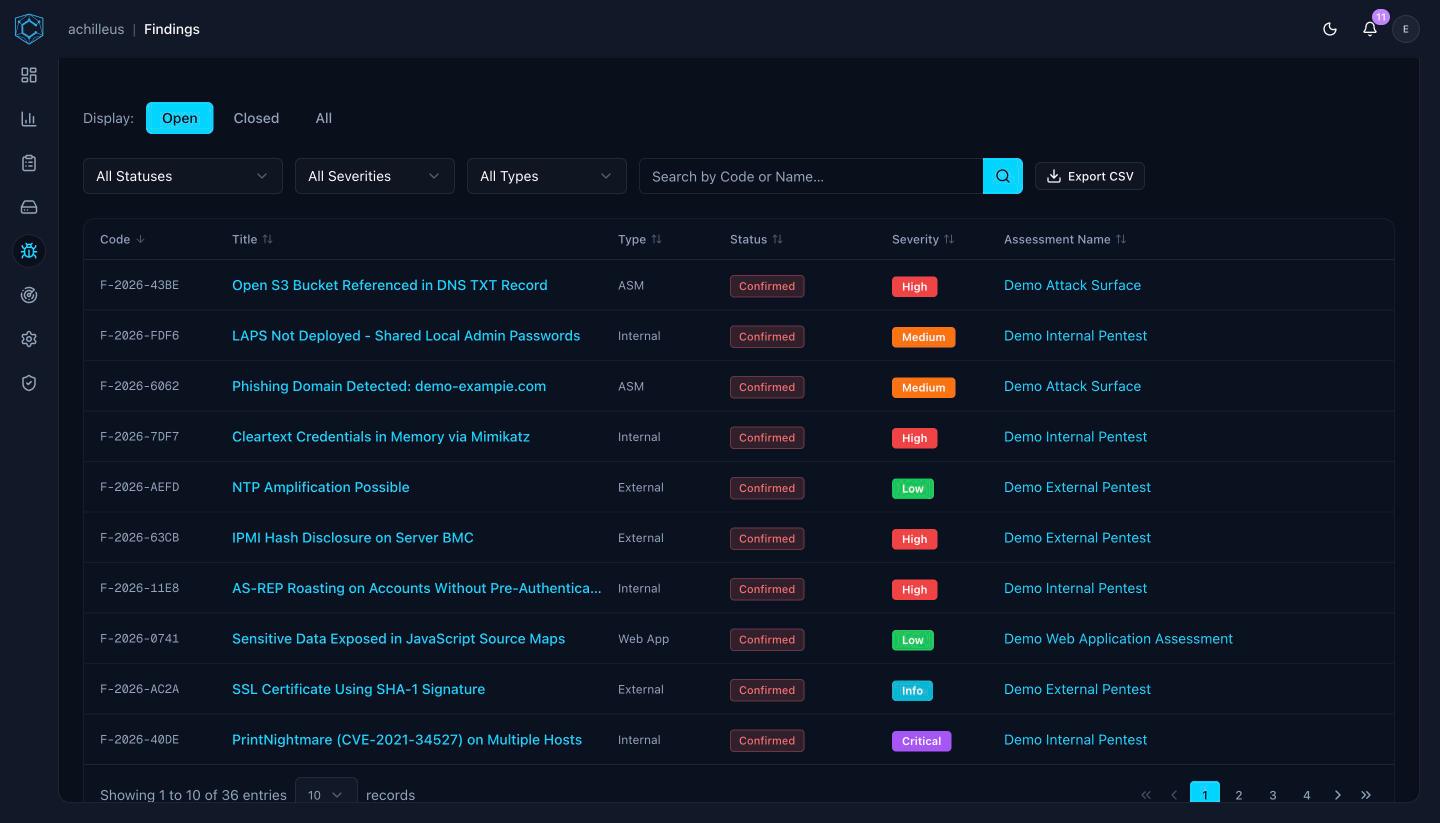
Every confirmed finding, in one queue.

Severity, status and the assessment it came from, across web, internal, external and ASM, ready to export to your tracker.

Canima portal · Findings
Canima findings table listing confirmed findings across ASM, internal, external and web app assessments
02 / Assessment pipeline

One knowledge graph. Agents see what scanners cannot.

Endpoints, parameters and technologies are linked in one graph, so each specialized agent targets the inputs where its vulnerability class can actually live.

Project graph · step 01 / 05
01

Discovery & Application Mapping

Spider agents crawl the application using headless browser automation, navigating JavaScript-heavy SPAs, intercepting AJAX calls, evaluating the DOM, and capturing WebSocket traffic. Archive-based URL discovery and JavaScript static analysis supplement the crawl. Every endpoint, parameter, header, and cookie is indexed in the knowledge graph as interconnected nodes.

02

Baseline & Technology Fingerprinting

Fingerprinting agents identify frameworks, libraries, server technologies, and their exact versions. CVEs are mapped against detected versions with exploit availability data. The graph is enriched with technology nodes linked to their known vulnerability classes, informing which specialized agents should prioritize which endpoints.

03

Vulnerability-Specific Agent Deployment

Dedicated agents deploy in parallel: the SQLi agent targets parameters the graph has marked as database-backed, the XSS agent focuses on reflected output points, the SSRF agent tests URL-type parameters, and the auth agent probes access control boundaries. Each agent writes confirmed findings back to the graph with full request/response evidence, enabling cross-vulnerability chain detection.

04

Validation & Reporting

QA agents re-verify every finding, eliminating false positives. Each confirmed vulnerability gets CVSS scoring, CVE/CWE classification, affected URL and parameter detail, full reproduction steps with request/response captures, and specific remediation guidance. Reports include a vulnerability type distribution chart, security score, and executive summary alongside deep technical detail.

03 / Why Canima

Beyond DAST: Agent-Driven Application Security

DAST scanners run predetermined checks against every parameter and call it done. Canima deploys specialized agents that understand vulnerability context, adapt their payloads to the injection point, and coordinate through a shared knowledge graph to find what automated scanners fundamentally cannot.

01

One Agent Per Vulnerability Class

The XSS agent is fine-tuned for XSS and nothing else. It understands HTML injection contexts, JavaScript execution sinks, DOM mutation patterns, and WAF bypass techniques. This domain specificity produces findings that generic scanning engines miss because they spread attention across every vulnerability type simultaneously.

02

Headless Browser for Modern Apps

Single-page applications, client-side routing, and JavaScript-rendered content are invisible to traditional scanners. Canima's spider agents use full headless browser automation, executing JavaScript, handling authentication flows, intercepting API calls, and capturing dynamically rendered endpoints that static crawlers cannot see.

03

Context-Aware Payload Generation

Generic scanners fire the same payload list at every input. Canima's agents analyze the injection context first (is this inside an HTML attribute, a JavaScript string, a JSON body, a SQL WHERE clause?) then generate payloads specifically crafted for that context, dramatically increasing both detection rate and accuracy.

Capability comparison: Canima versus other tools
Capability Canima Others
Dedicated agent per vulnerability class Yes No
Context-aware payload generation Yes No
Live knowledge graph correlation Yes No
Full SPA/headless browser support Yes No
GraphQL & WebSocket testing Yes No
Cross-vulnerability chain detection Yes No
Proof-of-concept for every finding Yes No
Scheduled recurring assessments Yes No
04 / Questions
Can you test authenticated areas and multiple roles?

Yes. Every role in scope is authenticated, so access-control flaws like IDOR and privilege escalation are tested between real accounts.

Do you handle single-page apps and APIs?

Yes. Spider agents drive a headless browser through JavaScript-heavy SPAs and capture REST, GraphQL and WebSocket traffic.

What counts as one application?

One authentication boundary and one codebase, however many hostnames it runs on. app., admin. and api. on one codebase is one application.

How is this different from a DAST scanner?

DAST fires the same checks at every input. Canima’s agents read the injection context first, craft payloads for it, and validate each finding with proof-of-concept evidence.

See how a web application engagement unfolds.

Start your free 7-day demo to see how Canima goes deep into your applications with vulnerability-specific AI agents that find what scanners miss.