Internal & Active Directory
Kerberoasting, NTLM relay, BloodHound path analysis and lateral movement, chained from first foothold to Domain Admin.
KerberosNTLM relayBloodHoundDCSync
Explore Internal & Active Directory
Specialized AI agents attack your network, perimeter and apps around the clock. Every finding is safely exploited and proven.
PROOFOpen a real finding: NTLM relay → Domain AdminNeither shows how far an attacker could actually get today, from a first foothold to Domain Admin and your most sensitive data. Canima runs the engagement continuously, chains findings into real attack paths, and only reports what it has proven.
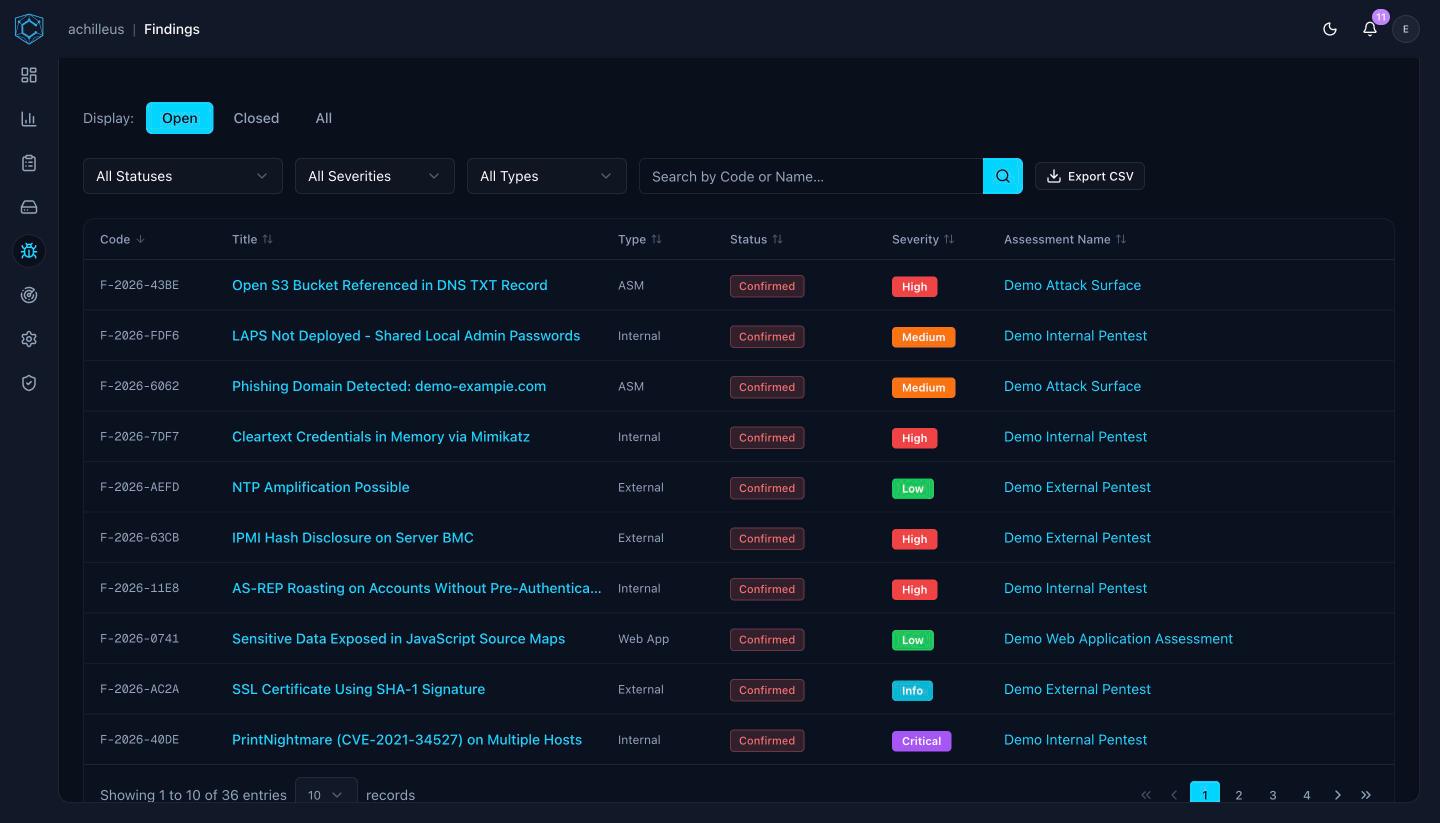
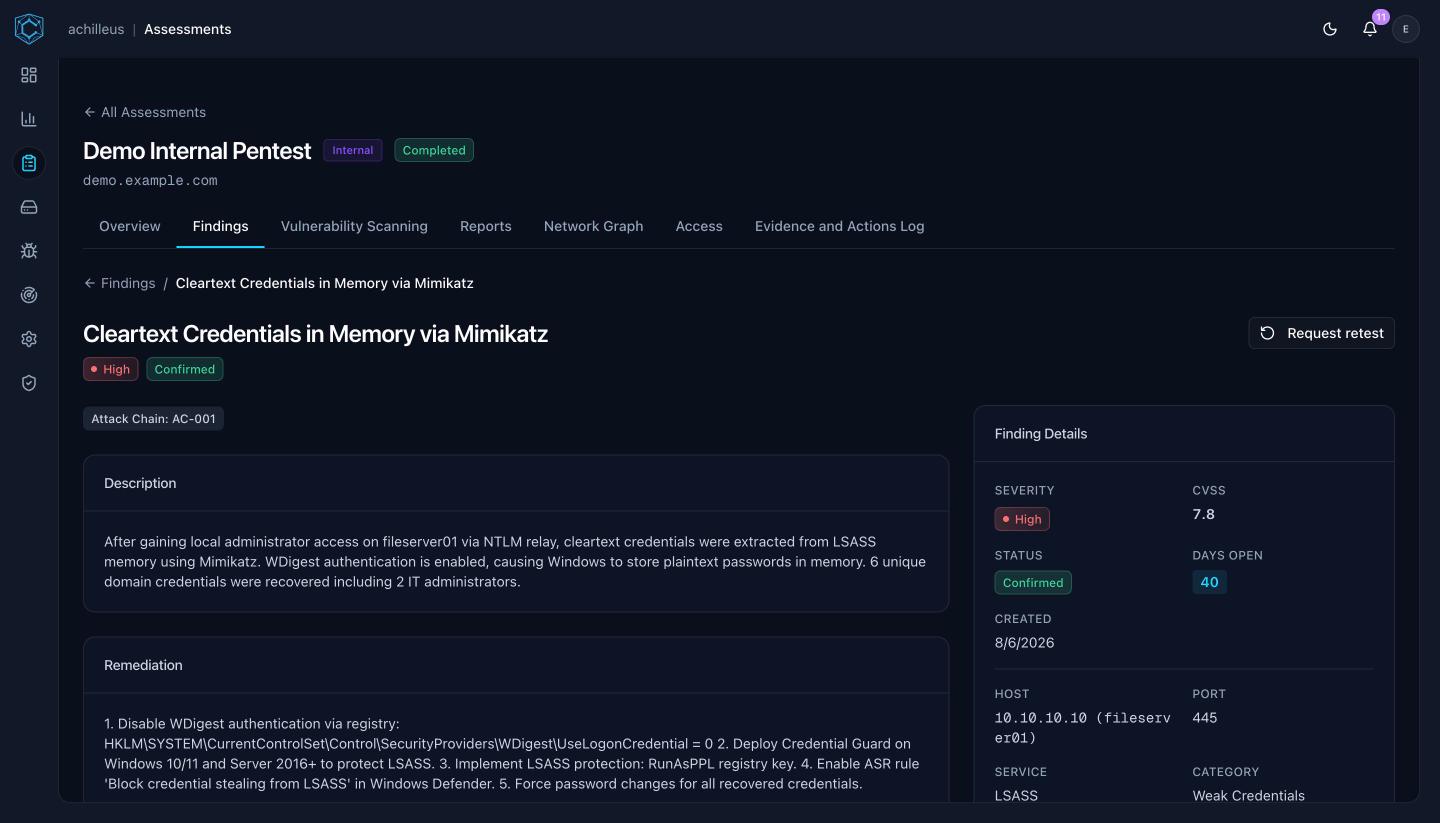
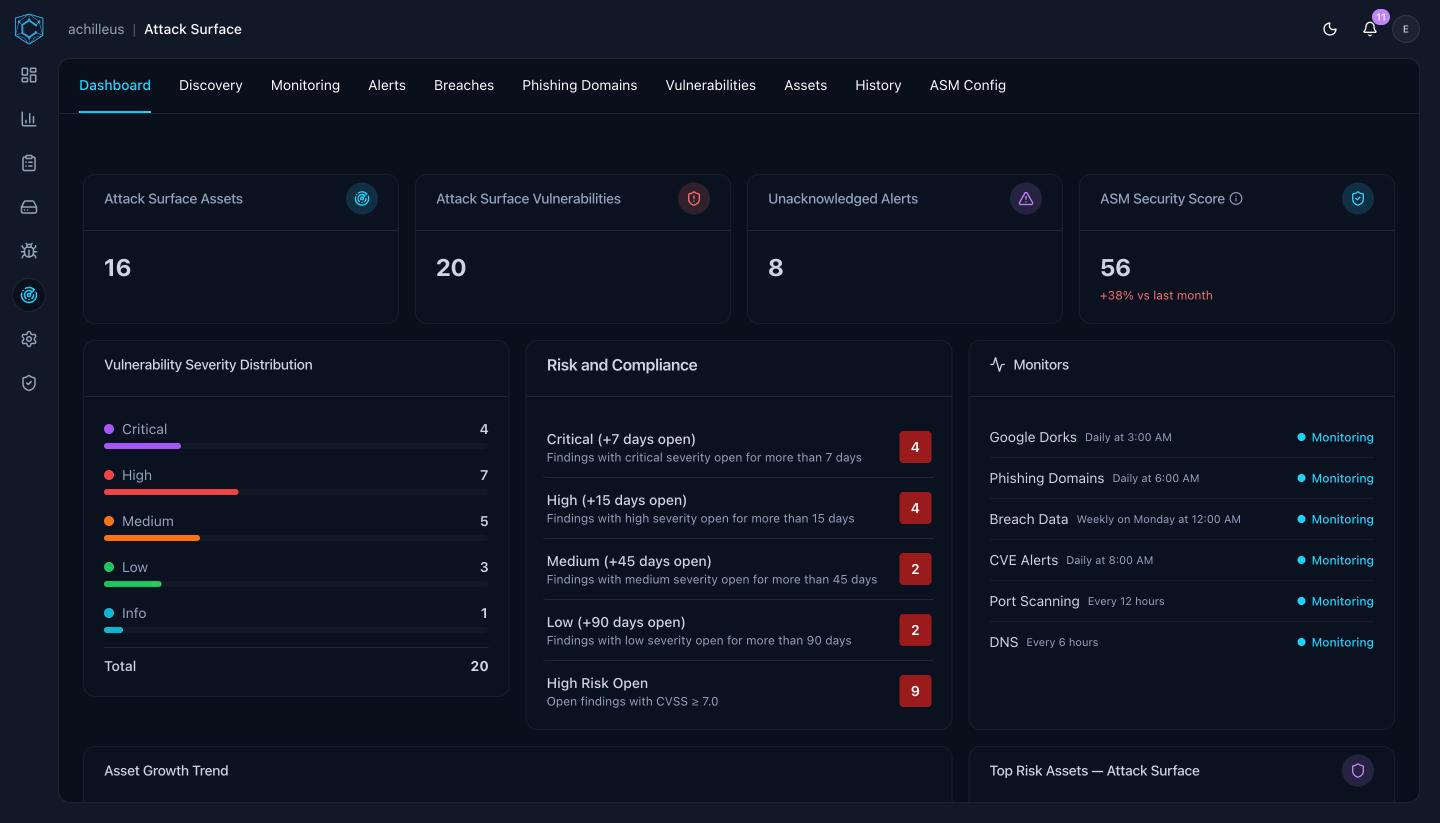
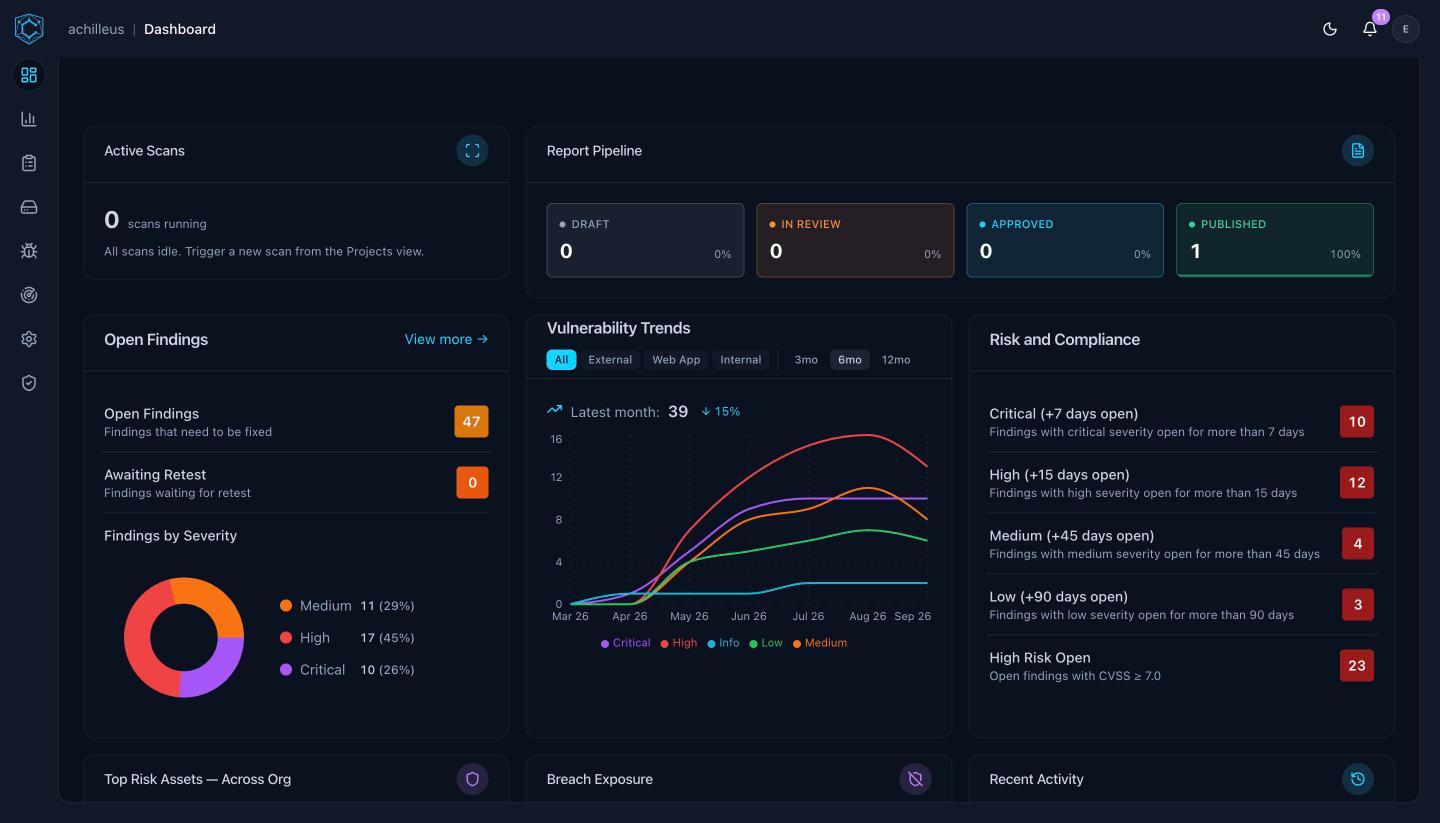
Findings, attack chains, retests and reports from every engagement. These are real screens from a demo tenant.
One view across every engagement.
Every row is confirmed, across all four surfaces.
Proof, context and the fix on one page.
Your perimeter, watched continuously.
Kerberoasting, NTLM relay, BloodHound path analysis and lateral movement, chained from first foothold to Domain Admin.
Subdomain recon, exposed services and leaked-credential monitoring. New exposures are tested as they appear.
Business logic, authentication flows and API chains, tested per application with every role authenticated.
Specialized agents map hosts, identities and apps, then attack in parallel through a shared knowledge graph.
Nothing is reported until it is exploited safely. Each finding carries proof-of-concept evidence.
Findings ship as end-to-end paths with CVSS, remediation guidance and compliance-ready reports.
Fix it, click retest. Verification never consumes your limits or application slots.
Canima was designed from the ground up by offensive security experts who think like attackers. This hacker-first approach ensures authentic attack replication and real-world threat modeling at scale.
Hundreds of specialized AI agents trained on real-world breaches from hundreds of offensive engagements. Each agent understands your environment: how authentication flows work, where privilege boundaries exist, and which business logic could be exploited, spotting sophisticated threats automated scanners miss.
Weekly updates from live CVE feeds, dark web data, and ongoing real-world offensive engagements. Every finding is automatically validated through safe exploitation, delivering only actionable, exploitable vulnerabilities with proof-of-concept evidence. 99.9% reduction in false positive triage.
Built by Elias Marquez, founder of Achilleus penetration testing firm. Every attack chain, privilege escalation path, and lateral movement technique comes from hundreds of real-world engagements, not theoretical databases. This is adversarial thinking encoded at scale.
| Capability | Canima | Others |
|---|---|---|
| Autonomous exploitation chains | Yes | No |
| Human-like decision making | Yes | No |
| Context-aware attack paths | Yes | No |
| Real pentester methodology | Yes | No |
| Adaptive engagement logic | Yes | No |
| Expert escalation when needed | Yes | No |
The Kerberos agent thinks only about Kerberos. Active agents (cyan) are running on engagements right now.
Test continuously across internal and external networks without booking an outside firm.
Learn more MSP / MSSPMulti-tenant, co-branded reports and complete data isolation between clients.
Learn more Pentest firmsLet agents handle recon and initial exploitation so your people go deeper.
Learn more ComplianceEvidence-backed reports auditors accept, refreshed every month.
Learn moreCanima encodes a decade of real engagement methodology. Every attack chain and escalation path comes from work on real networks, not theoretical models.
Domains and IPs for network testing. Per application for web apps. Retesting is always free.
From 2 domains and 10 assets. Monthly limits.
From 100 IPs. No minimum asset count.
12 assessments a year per app, unlimited retests.
No. The multi-tenant platform keeps complete data isolation between tenants, including for MSPs running many clients from one dashboard.
No. Canima runs proprietary models and calls no third-party AI APIs.
Yes. Agents use safe exploitation techniques designed for production, and you can set risk tolerance per engagement.
Every finding is validated by safe exploitation and delivered with proof-of-concept evidence. Edge cases escalate to human QA.
Nothing. Retesting is free on every plan and never consumes limits or application slots.
No. Explore the platform in a self-serve demo with sample data. SSO is included on every plan.
Autonomous penetration testing. Validated, continuous, real.