Your attack surface, mapped and proven, around the clock.
Your internet-facing infrastructure is the first thing attackers probe. Canima pairs deep external penetration testing with continuous attack surface monitoring, so every new exposure is found, tested and proven as it appears.
Full external attack surface, covered and monitored.
From initial reconnaissance through controlled exploitation, then continuous monitoring that never sleeps. Every internet-facing asset is discovered, tested, and tracked.
Reconnaissance & Asset Discovery
Automated discovery of all internet-facing assets including domains, subdomains via certificate transparency and DNS brute-forcing, IP ranges, open ports, and running services. OSINT gathering includes email harvesting, GitHub secret scanning, Google dorking, and public data exposure. Every discovered asset becomes a node in the knowledge graph.
Cross-validates findings across industry-leading scanners (Nuclei, OpenVAS, Nessus) to minimize false positives. Deep service enumeration across SMB, SNMP, LDAP, RPC, HTTP/S, DNS, FTP, SSH, RDP, VPN/IPsec, and more. Version-level CVE mapping with exploit availability tracking so you know which vulnerabilities are weaponized, not just theoretical.
NucleiNessusOpenVASCVE Mapping
Controlled Exploit Validation
Confirmed vulnerabilities are validated through controlled exploitation, not just flagged as "potentially vulnerable." Credential testing against discovered services covers default credentials, weak passwords, and password spraying. VPN and IPsec endpoint security is assessed for cryptographic weaknesses and configuration flaws.
MetasploitHydraCredential TestingVPN Assessment
Continuous Attack Surface Monitoring
ASM runs 24/7 with configurable cron schedules per monitor type. Detects newly opened ports, DNS changes, subdomain takeover opportunities, new CVEs affecting your deployed versions, and unauthorized record modifications. First-seen and last-seen timestamps track asset lifecycle with active, inactive, new, and changed status tracking.
Port MonitoringDNS ChangesCVE TrackingSubdomain Takeover
Dark Web & Breach Intelligence
Breach monitoring agents scan stealer log dumps, dark web marketplaces, credential databases, and paste sites for your organization's exposed data. Results include source classification (stealer, dark web, credential dump), affected email addresses, password exposure flags, and employee vs. consumer classification to prioritize response.
Stealer LogsCredential DumpsDark WebBreach Triage
Phishing & Brand Protection
Phishing detection agents monitor for lookalike domain registrations and active phishing infrastructure targeting your brand. Google dork monitoring detects sensitive files, admin panels, and configuration data exposed via search engine indexing. Real-time alerting with severity classification ensures you see threats before your users do.
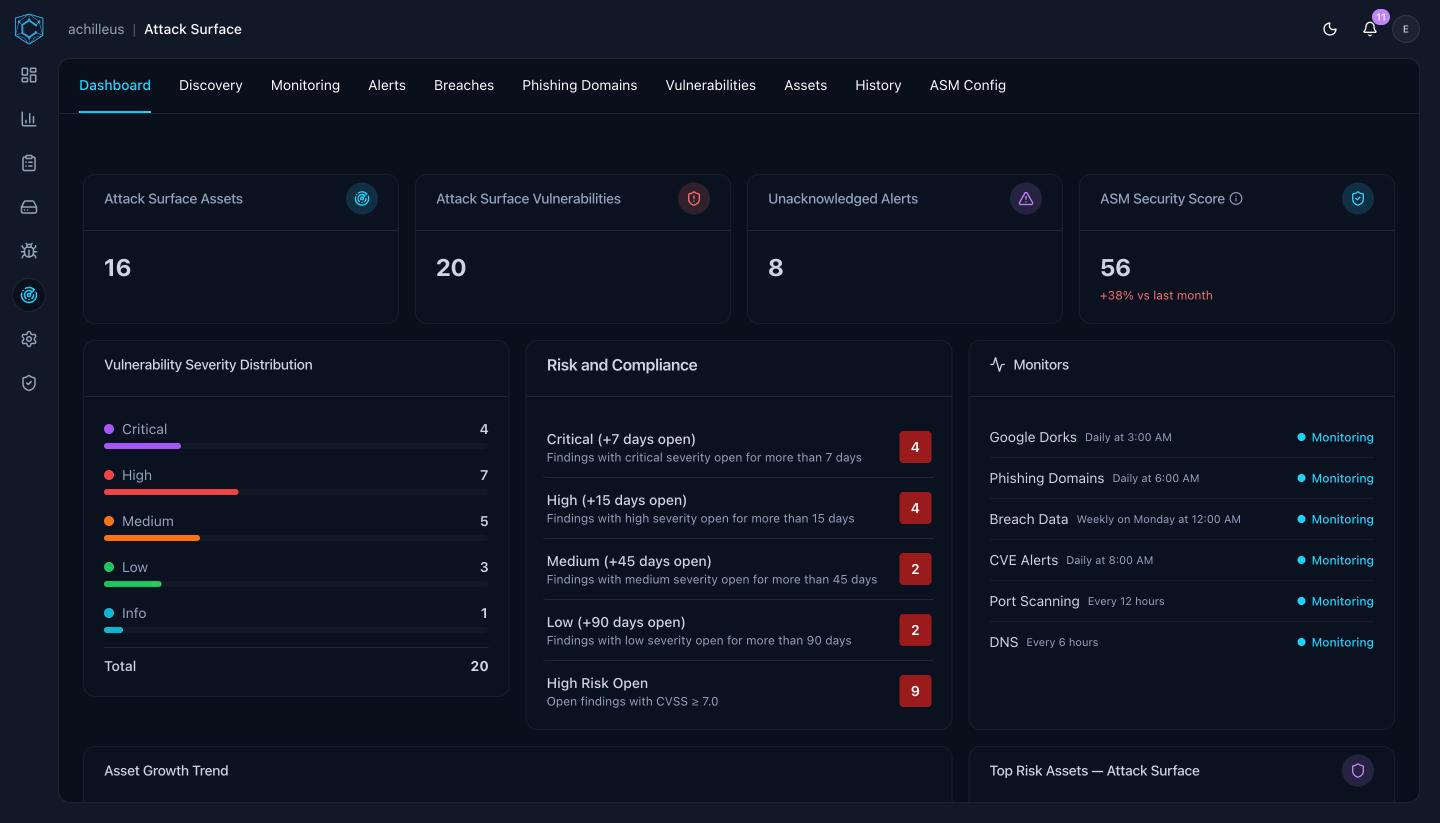
Asset counts, severity across the perimeter, and every active monitor, from breach data to lookalike domains, in one view.
Canima portal · Attack surface
02 / Assessment pipeline
One knowledge graph. Every finding correlated.
A vulnerable service is linked back to its domain, IP and network context, so agents know what is actually exposed and what an attacker could chain next.
Project graph · step 01 / 05
01
Discovery & Reconnaissance
Recon agents enumerate your full external footprint: domains, subdomains, DNS records, IP ranges, open ports, and running services. OSINT agents harvest emails, scan GitHub for leaked secrets, and run Google dork queries. Every asset is indexed in the knowledge graph with relationship edges connecting domains to IPs to services.
02
Enumeration & Vulnerability Assessment
Service-specific agents perform deep enumeration across every discovered protocol. Multiple vulnerability scanning engines run in parallel and cross-validate findings to eliminate false positives. CVEs are mapped to exact versions with exploit availability and CVSS scoring. Results flow into the graph where agents can correlate a vulnerable service back to its domain, IP, and network context.
03
Exploitation & Validation
Exploit agents read confirmed vulnerabilities from the graph and perform controlled exploitation to validate real-world exploitability. Credential testing agents spray discovered services with default and weak passwords. Each validated finding gets proof-of-concept evidence and reproduction steps. The graph distinguishes between theoretical and confirmed-exploitable vulnerabilities.
04
Continuous ASM Monitoring
After the initial assessment, ASM agents run on configurable schedules: port monitors, DNS monitors, CVE monitors, breach monitors, phishing monitors, and dork monitors. Each check compares against baseline state in the graph. New assets, changed configurations, fresh CVEs, and detected breaches trigger real-time alerts with severity classification.
03 / Why Canima
Beyond Scanning: Intelligent Offensive Security
Traditional external assessments run a scanner and hand you a PDF. Canima deploys hundreds of specialized agents that coordinate through a shared knowledge graph, cross-validate findings across engines, and then keep watching your attack surface 24/7.
01
Pentest + ASM in One Platform
Deep penetration testing and continuous attack surface management are not separate products. They share the same knowledge graph, the same agent infrastructure, and the same dashboard. Your initial assessment becomes the baseline for ongoing monitoring.
02
Multi-Engine Cross-Validation
Canima does not rely on a single scanning engine. Multiple industry-leading tools run in parallel, and findings are cross-validated through the knowledge graph. A vulnerability flagged by one engine and confirmed by another has a fundamentally different confidence level than a single-source finding.
03
Controlled Exploitation, Not Just Detection
Flagging a CVE as "potentially vulnerable" is not enough. Canima's exploit agents validate confirmed vulnerabilities with controlled payloads and document proof-of-concept evidence. You know what is actually exploitable, not what might be.
Capability comparison: Canima versus other tools
Capability
Canima
Others
Multi-engine cross-validated scanning
✓Yes
—No
Controlled exploit validation with PoC
✓Yes
—No
Live knowledge graph correlation
✓Yes
—No
Integrated ASM with pentest baseline
✓Yes
—No
Dark web & breach monitoring
✓Yes
—No
Phishing & lookalike domain detection
✓Yes
—No
Configurable monitor schedules
✓Yes
—No
Agent activity logs with proof
✓Yes
—No
04 / Questions
Will scanning disrupt our production services?
No. Agents throttle their scans and validate findings with controlled, non-destructive exploitation. You set the risk tolerance per engagement.
How often is the attack surface checked?
Continuously. Port, DNS, CVE, breach, phishing and dork monitors run on schedules you configure, and new exposures are tested as they appear.
What counts toward our plan limits?
Root domains monitored and live assets (IPs or subdomains) tested each month. Retesting never consumes limits.
Do you test VPN and remote-access endpoints?
Yes. VPN and IPsec endpoints are assessed for cryptographic weaknesses and configuration flaws, and discovered services are tested for default and weak credentials.
See how an external engagement unfolds.
Start your free 7-day demo to see how Canima discovers every internet-facing asset, validates real vulnerabilities, and monitors your attack surface around the clock.