From foothold to Domain Admin, proven step by step.
What happens after an attacker breaches your perimeter? Canima maps your internal network, attacks Active Directory, moves laterally and escalates. Every credential, pivot and escalation step is documented with proof.
Real attackers do not stop at one host. Neither do we.
Active Directory Attack Surface
Full AD enumeration including users, groups, trusts, GPOs, delegation configurations, and ACL-based privilege escalation paths. Identifies Kerberoastable SPNs, AS-REP roastable accounts, unconstrained delegation, and resource-based constrained delegation misconfigurations that real attackers chain together for domain compromise.
KerberoastingAS-REP RoastingRBCDDCSync
Credential Attacks & Hash Cracking
Lockout-aware password spraying across LDAP, SMB, RDP, and Kerberos. LLMNR/NBT-NS poisoning for NTLMv2 capture. Offline hash cracking with Hashcat against captured Kerberos TGS tickets and NTLM hashes. Every cracked credential feeds back into the knowledge graph for downstream agents to leverage.
Password SprayingLLMNR PoisoningNTLMv2Hashcat
Lateral Movement & Pivoting
Pass-the-hash, pass-the-ticket, overpass-the-hash, and credential forwarding across your network. The lateral movement agents consume cracked credentials and session tokens from the knowledge graph in real time, pivoting through hosts to reach high-value targets like database servers, file shares, and domain controllers.
Pass-the-HashPass-the-TicketWMI ExecPSRemoting
NTLM Relay & Protocol Exploitation
Identifies and validates NTLM relay opportunities across SMB, LDAP, and HTTP. Tests for coercion vulnerabilities like PetitPotam and PrinterBug to force authentication from privileged accounts. Covers SMB signing enforcement, LDAP signing, EPA configuration, and channel binding gaps.
NTLM RelayPetitPotamPrinterBugSMB Signing
Local Privilege Escalation
On every compromised host, agents enumerate kernel vulnerabilities, misconfigured services, unquoted service paths, writable DLL directories, token impersonation opportunities (SeImpersonate, SeAssignPrimaryToken), and AlwaysInstallElevated policies. Each escalation path is validated, not just flagged.
Complete internal network mapping across subnets and VLANs. Deep service enumeration on SMB, LDAP, SNMP, SSH, RDP, FTP, MySQL, PostgreSQL, MSSQL, MongoDB, and Oracle. Tests for default credentials, anonymous access, and known CVEs (EternalBlue, SMBGhost, ZeroLogon, BlueKeep) with controlled exploitation.
EternalBlueZeroLogonBlueKeepDefault Creds
In the portal
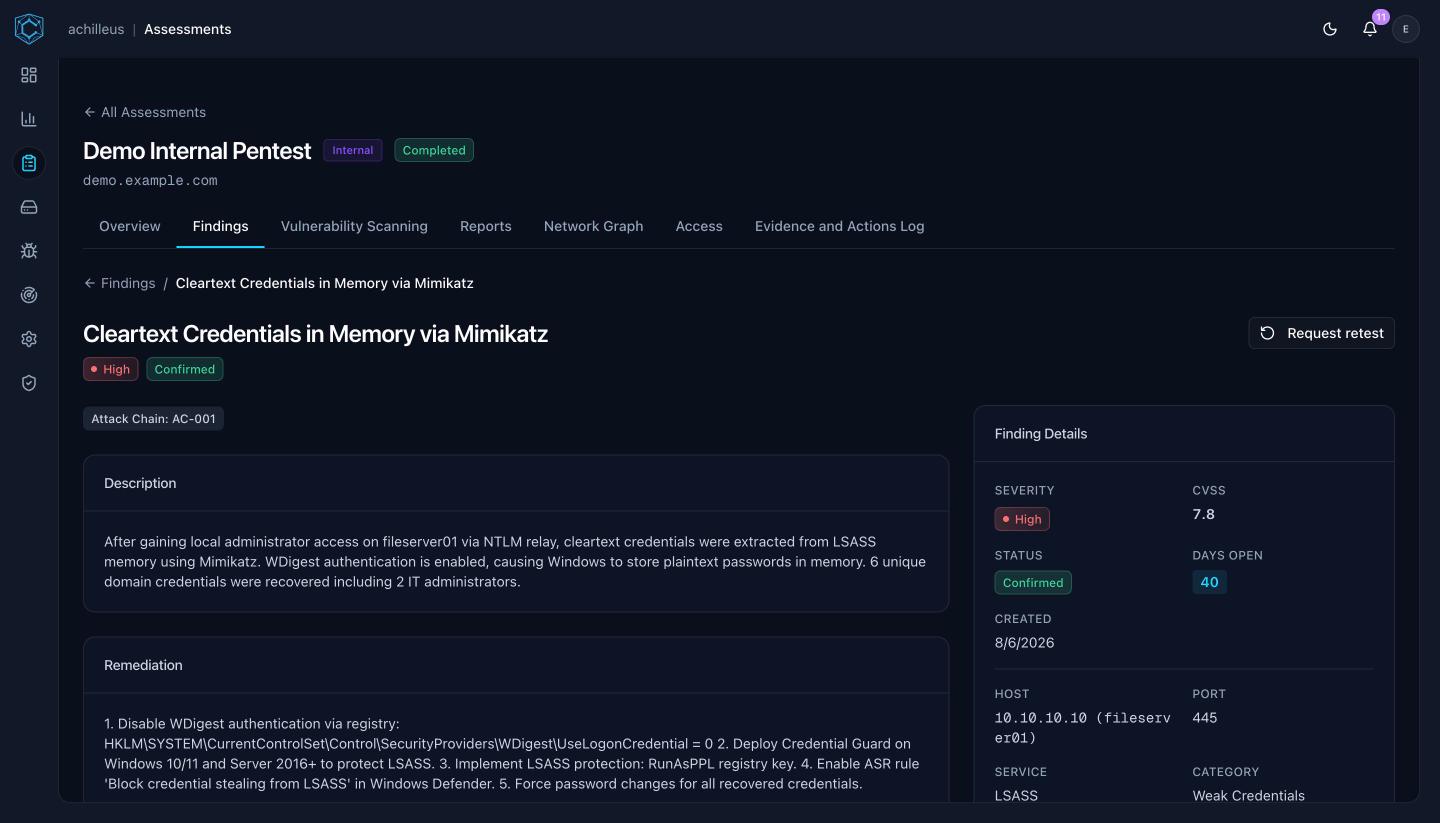
One hop of the chain, as your team sees it.
Confirmed severity, the attack chain it belongs to, host-specific remediation, and a free retest button.
Canima portal · Demo Internal Pentest · Finding
02 / Assessment pipeline
One knowledge graph. Every agent reads it.
When the Kerberos agent cracks a hash, the lateral movement agent knows instantly. That is how real attack chains emerge.
Project graph · step 01 / 05
01
Reconnaissance & mapping
Discovery agents map subnets, hosts and services. AD agents pull users, groups, trusts, SPNs and GPOs into the knowledge graph.
02
Vulnerability & credential attacks
Kerberos, spraying, LLMNR and CVE agents launch in parallel. Captured credentials are pushed to the graph instantly.
03
Exploitation & lateral movement
Exploit agents validate with controlled payloads. Lateral movement agents pivot using pass-the-hash, pass-the-ticket and relay.
04
Privilege escalation & reporting
DCSync, golden ticket and trust paths. Every step from foothold to Domain Admin documented with PoC, then QA-reviewed.
03 / Why Canima
Built Different From Traditional Pentesting
Traditional internal pentests give you a snapshot from one consultant with limited time. Canima gives you exhaustive coverage from hundreds of domain-specific AI agents that coordinate, share intelligence, and chain attacks like a real adversary.
01
Domain-Specific Agent Architecture
Every vulnerability class gets a dedicated AI agent fine-tuned for that domain. The Kerberos agent thinks only about Kerberos. The NTLM relay agent focuses solely on relay paths. No context rot, no generic scanning. Expert-level depth across every attack surface.
02
Knowledge Graph Intelligence
A live Neo4j-style graph database connects every finding. Agents write discoveries as nodes and edges, then query the graph to make informed decisions. This is how a cracked SPN hash leads to a lateral movement path that leads to domain admin, automatically.
03
Full Attack Chain Documentation
Every path from initial access to domain compromise is documented end-to-end with timestamps, credentials used, tools invoked, and proof-of-concept evidence. Your report does not just list vulnerabilities. It shows exactly how they chain together.
Capability comparison: Canima versus other tools
Capability
Canima
Others
Hundreds of specialized agents
✓Yes
—No
Live knowledge graph correlation
✓Yes
—No
Automated attack chain building
✓Yes
—No
Real-time credential propagation
✓Yes
—No
Full AD attack surface coverage
✓Yes
—No
Controlled exploit validation
✓Yes
—No
Agent activity logs with proof
✓Yes
—No
Cross-assessment trending
✓Yes
—No
04 / Questions
Will password spraying lock out our users?
No. Spraying is lockout-aware and throttled across LDAP, SMB, RDP and Kerberos.
What does proof of Domain Admin look like?
A complete attack chain with timestamps, credentials used, tools invoked and proof-of-concept evidence for every step.
How small can our network be?
There is no minimum asset count. Internal plans start at 100 live IPs a month.
Can it run on-premise?
Yes. On-premise deployment is available on internal plans.
See how an internal engagement unfolds.
Start your free 7-day demo to see how Canima maps your Active Directory attack surface, chains credential attacks, and documents every path to domain compromise.